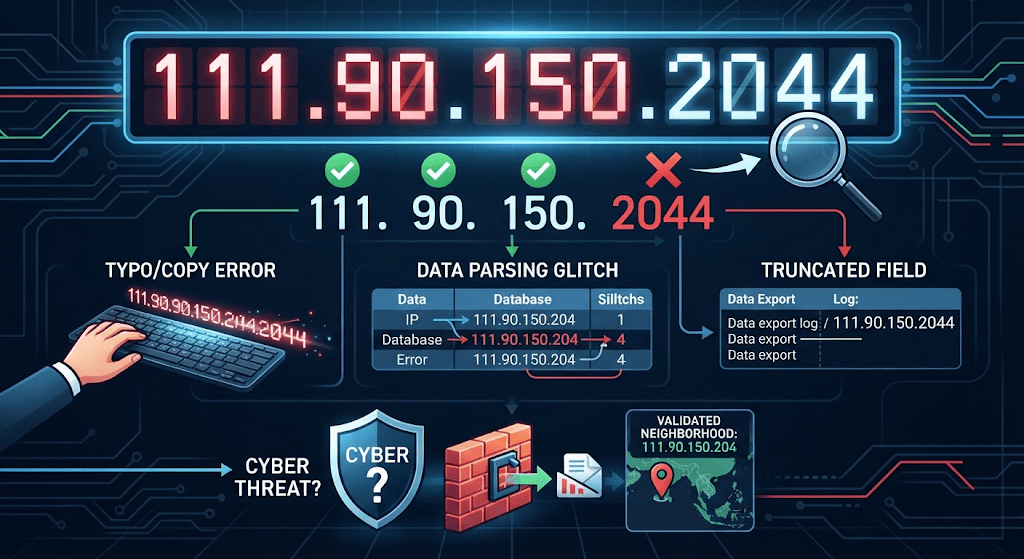
Ever stumbled upon a bizarre string of digits in your server logs or a tech forum and wondered what on earth it means? If you have recently encountered 111.90.150.2044, you are definitely not alone. At first glance, it looks like a standard network address, but a closer technical look reveals something quite unusual.
Let’s dive straight into what this string is, why it trips up system administrators, and whether you actually need to panic.
Why 111.90.150.2044 Is Not a Valid IP Address
To understand why this string catches people off guard, we need to look at how the internet structures its identifiers. Standard IPv4 addresses rely on a very strict mathematical format.
- The Four Octet Rule:An IPv4 address contains four distinct numerical sections, known as octets, separated by periods.
- The Numerical Limit:Each individual octet must fall strictly between 0 and 255.
When you break down 111.90.150.2044, the first three sections ($111$, $90$, and $150$) fit comfortably within the rules.However, the final section is 2044. Because 2044 vastly exceeds the maximum allowable limit of 255, this string fails standard network validation.In plain terms, it is technically an invalid IPv4 address.
Common Causes Behind Malformed IP Strings
If it isn’t a working destination address, how does a string like 111.90.150.2044 end up floating around in web traffic analytics, GitHub snippets, or error reports? Usually, it comes down to a few common digital hiccups:
- Typographical and Copy Errors: A slip of the finger while copying text or manually typing out a configuration can easily merge numbers together.
- Data Parsing Glitches:Automated scripts and log parsers sometimes stitch adjacent database values or port numbers onto the end of a legitimate IP address.
- Truncated Data Fields: Software exporting raw telemetry data might clip text boundaries, fusing an IP prefix with an extraneous digit string.
Is It a Cyber Threat or Malware?
When people see a weird network-looking string, cybersecurity fears often bubble to the surface. Is it a hacker knocking at your digital door?
Generally speaking, an invalid IP format by itself does not mean an attack is underway.Because 111.90.150.2044 cannot function as a real routing destination on the internet, malicious bots cannot use it to establish a direct connection.
However, security researchers note that looking at the beginning of the string can sometimes point toward a real neighborhood. If you trim off the error and look at 111.90.150.204, that truncated base resolves to a legitimate block of addresses historically tied to hosting providers in Southeast Asia. Seeing the malformed version usually points to a logging glitch rather than an active breach.
Frequently Asked Questions
Can I run a geolocation lookup on 111.90.150.2044?
No. Standard geolocation databases require a valid, active IP structure to pinpoint a country or network.Because the final octet breaks formatting rules, lookup tools will return an error.
What should I do if I see this string in my firewall logs?
Don’t panic. Check your log parser or script configurations. It is almost always the result of a formatting error, copy-paste mistake, or data-merging glitch rather than a targeted intrusion.
Is 111.90.150.204 a real address?
Yes, removing the trailing error leaves behind a standard, valid IP format.However, you should never automatically assume the truncated version was the actual intended target without investigating your original data source.
Conclusion
Encountering an odd anomaly like 111.90.150.2044 can feel puzzling, but the mystery usually boils down to math and software syntax rather than malicious intent.Because the final numbers break the basic rules of IPv4 architecture, it remains a malformed string rather than a functional network route.
Have you recently run into other strange error codes or log anomalies? Feel free to explore our other technical troubleshooting guides to clear up more digital mysteries!